Stop cyberattacks before they spread across your network.
SEGVARD prevents what turns a breach into a crisis—stopped business operations, encrypted systems, and stolen data. We find network vulnerabilities that allow an attack to spread, and help you fix them.
Why SEGVARD
Devastating attacks spread through the firewall.
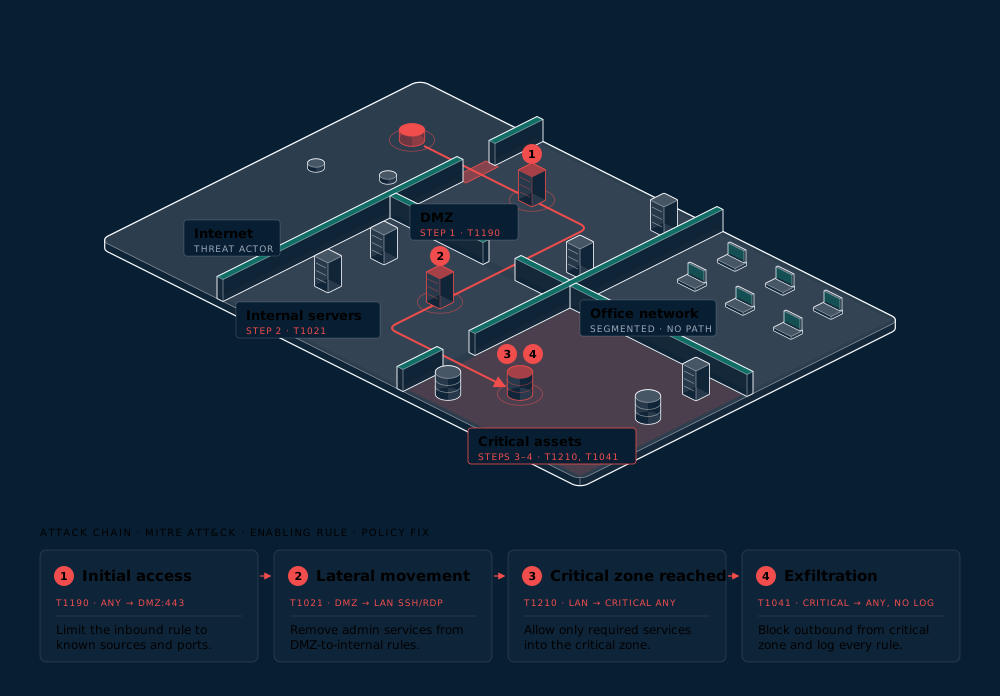
Attackers rarely stop at the first device. They move on to critical IT and production systems through rules that are too broad, temporary exceptions never removed, and missing segmentation. Each one is a path. The same weakness can be minor in one organisation and critical in another. SEGVARD starts by understanding your business, then finds these paths and helps you close them before they are used.
An assessment built on your business
We start by learning your business processes and IT/OT structure. Every conclusion about your network's security is drawn for your organisation, not from a generic checklist.
Know what your network really allows
We map your network’s real structure from the firewall configuration and check every rule against CIS Benchmarks. Each risk is linked to its exact configuration line.
Know which risks are critical
Severity is set by attack path modelling (MITRE ATT&CK): a risk is critical if it lets an attacker reach your critical systems. A certified expert confirms every finding.
Know what to fix first
You get prioritised recommendations to prevent each critical risk. No resources wasted on insignificant flaws. If needed, our engineers help your team implement the changes and confirm the risks are closed.
How it works
- 1
Confidential kick-off and configuration handover
Under NDA, we learn your business processes, critical systems and IT/OT structure. You send a sanitised export of rules, zones, objects and routes, without credentials or keys, over an encrypted channel.
- 2
Analysis and attack path modelling
Rule-based analysis of every rule, object and route. AI-assisted modelling links findings into attack paths and sets their severity for your environment. It runs on HCSECURITY's own infrastructure, with no cloud AI services.
- 3
Expert validation and report
A certified expert confirms every finding against your business context. You receive a report with prioritised recommendations (PDF/DOCX).
- 4
Implementation support (optional)
We help your team apply the fixes and verify the result.
- 5
Data deletion
Your data is deleted at project close, confirmed in writing.
Network Security Assessment includes
- 01
Analysis of your business processes and IT/OT structure
- 02
Network reconstruction from the firewall configuration
- 03
Rule assessment with CIS Benchmark references
- 04
Attack path modelling (MITRE ATT&CK) to set risk severity for your business
- 05
Prioritised recommendations for risk prevention
- 06
Certified expert confirmation of every finding
- 07
Implementation support, if needed
How far could an attack spread in your network?
Start with a confidential conversation. We sign an NDA before any data is shared, receive only the configuration we need over an encrypted channel, and delete it with written confirmation when the project closes.